

Fake orders are orders that nobody intends to pay for honestly: bots submitting forms, fraudsters testing stolen cards, pranksters, competitors and affiliates inflating their numbers. You spot them by the order fields (a made-up name, an impossible phone number, a burst of orders in a minute, failed card attempts) and stop them in three layers: bot protection on the website, payment checks such as 3D Secure, and a manual review of risky orders before shipping.
The fake that a manager cancels costs a few minutes. The expensive one is the order that passes every check, gets shipped and comes back as a chargeback: you lose the goods, the shipping and a dispute fee. Below: where fake orders come from, seven signs in the order itself, what they cost on illustrative numbers, and which checks real customers barely notice.
When store owners search for "fake orders"
Usually after a strange morning: a dozen orders with names like "asdf", emails that bounce, and a list of declined card payments in the payment dashboard. Or after a month when chargeback notices started to arrive for orders that had already shipped. The owner searches for "fake orders", "fraudulent orders" and "card testing", and then asks: "how do I stop bots placing orders", "should I cancel a suspicious order", "can I block a customer".
Most people want to find who is behind it. The more useful question is different: at which step should a fake order stop, so that it never costs you money.
Who places fake orders and why
Mostly bots and careless visitors, not organised criminals; deliberate attacks are rarer than forum threads suggest. The source decides where you catch the order.
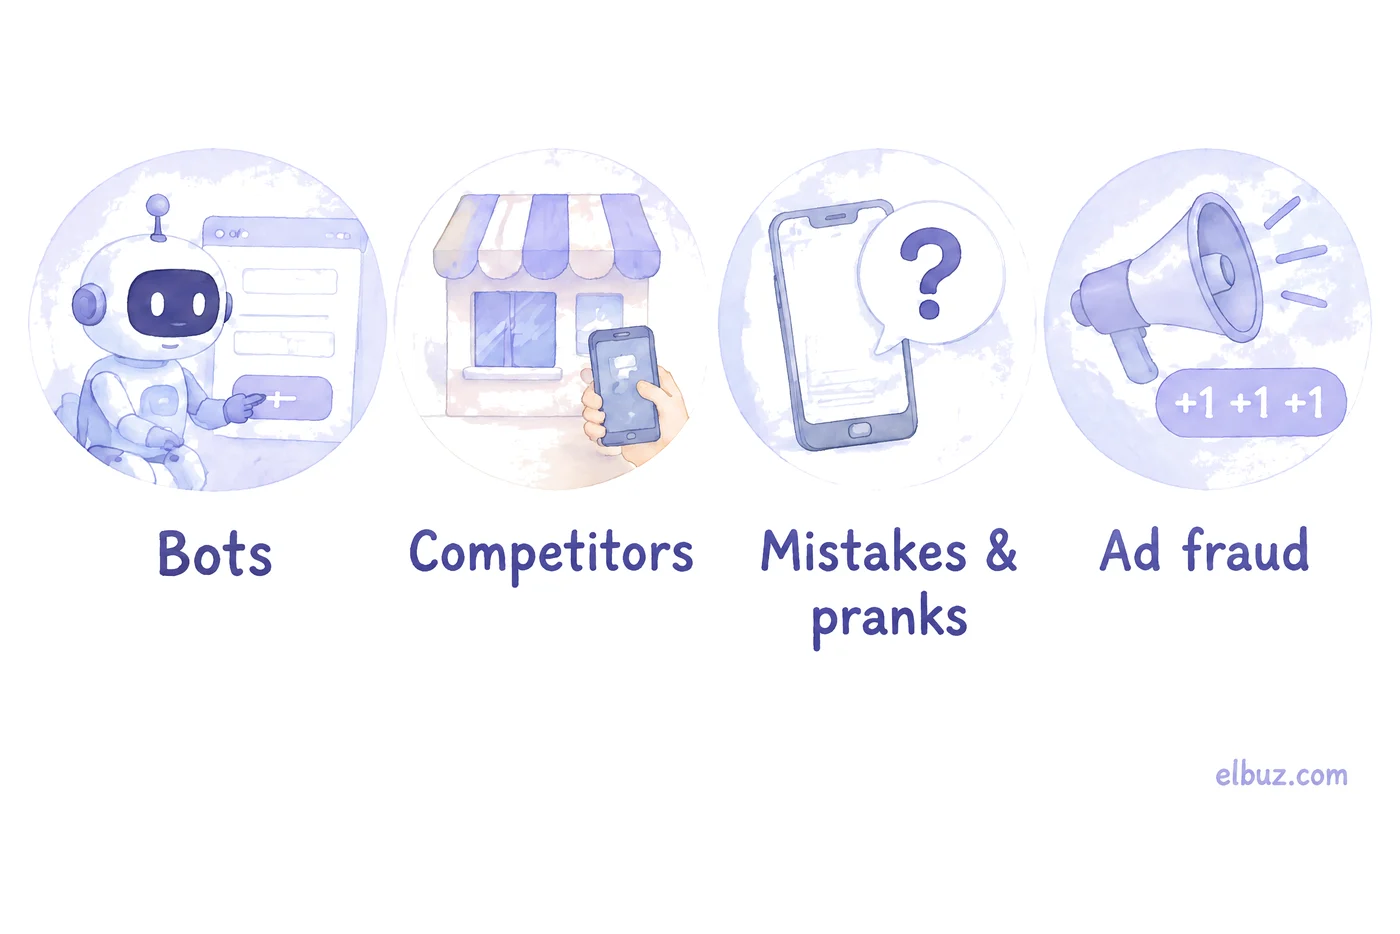
| Source | Why | What the order looks like | Where to stop it |
|---|---|---|---|
| Spam bots | probing forms, posting links | random letters in the name, links in the comment, dozens of orders in a row | website: CAPTCHA, hidden field |
| Card testers | checking which stolen card numbers still work | small amounts, many declined attempts, nonsense names and emails | website and payment: CAPTCHA, rate limits, 3D Secure |
| Mistakes and pranks | a child pressed the button, someone "tested how it works" | a real phone number, but nobody remembers the order | confirmation email or message |
| Competitors | tie up staff, check prices and terms, lock scarce stock in reservations | similar orders from different contacts for one scarce product | quantity limits, reserve stock only after payment or confirmation |
| Affiliate and ad fraud | a partner is paid per lead or per order | a spike of orders from one traffic source, conversion far above normal | analytics by source, pay partners only for paid orders |
| Fraudulent buyers | get the goods or the money back without paying | a normal order; the problem shows up later as a dispute or return | proof of delivery, return rules |
Card testing deserves a separate word. Stripe describes it as fraudsters checking whether stolen card details are valid, often with small payments and scripts that try many cards at once. Even failed attempts hurt: a spike in declines makes card issuers trust all your payments less, and the attempts that succeed come back as fraud disputes.
Seven signs of a fake or fraudulent order
One sign means little: a real customer can mistype an address too. Two or three together are a reason to hold the order and check it before you pack anything.
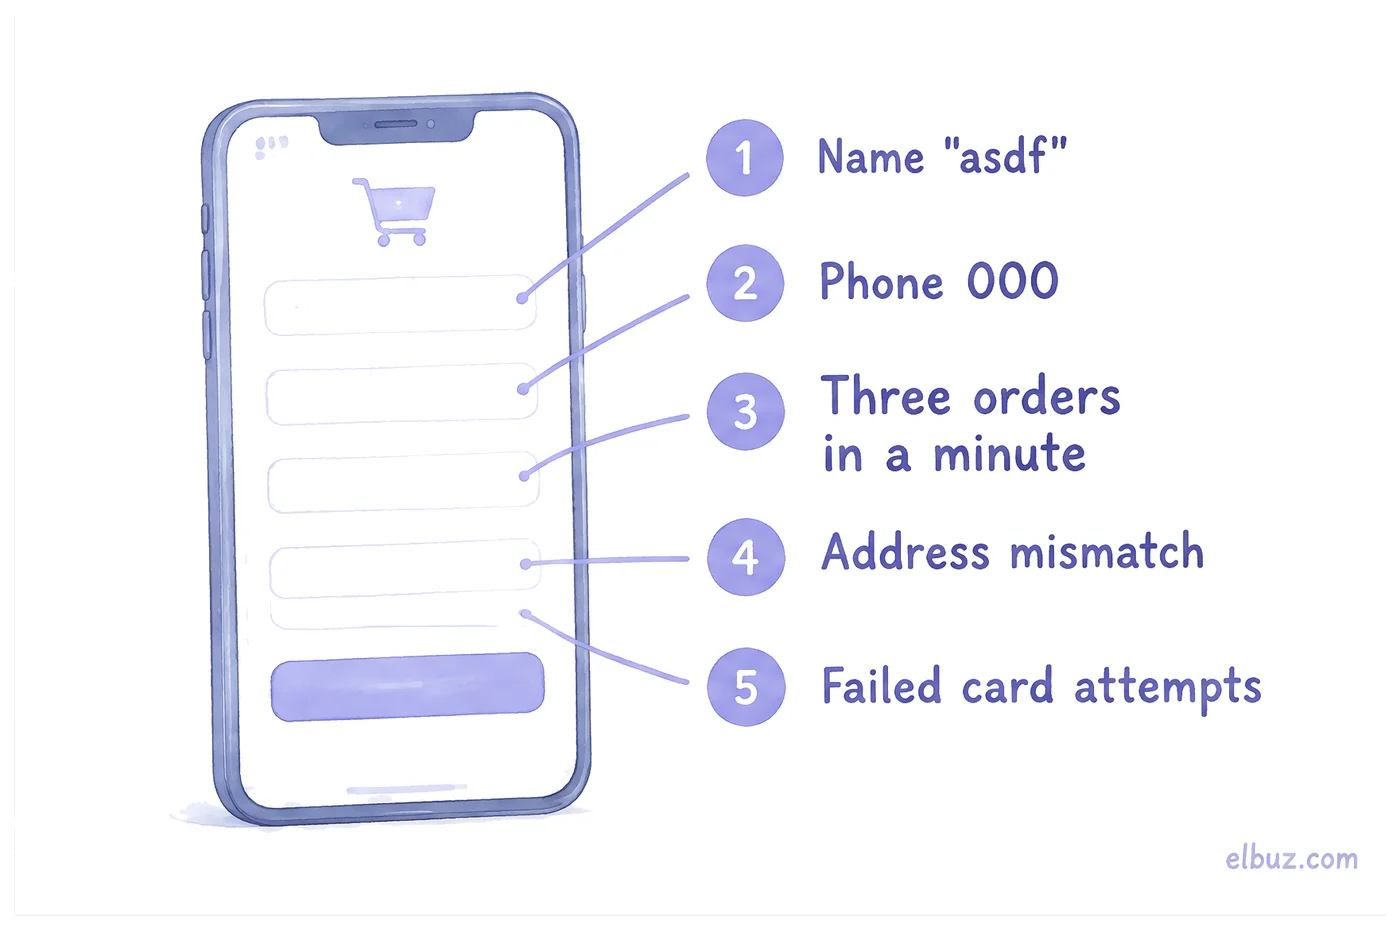
- A placeholder name or email. "asdf", "test", a string of random characters, an email that bounces.
- A phone number that cannot exist. All zeros, repeated digits, the wrong number of digits for the country.
- A burst of orders. Several orders from one email, device or IP address within minutes, often for the same product.
- Billing and shipping do not match. Different countries, or a shipping address that is a parcel forwarder far from the cardholder's address.
- Failed card attempts before a success. Several declines with different cards, then one payment goes through. Stripe lists a spike of failed payments and small payments with nonsense names as the typical picture of card testing.
- An unusual basket. Many units of an easily resold item, all sizes of one model, express shipping on a first order.
- A history of problems. This customer has already filed a chargeback or refused a cash-on-delivery parcel.
The first six are visible in the order itself. The seventh is the most reliable, but only if orders are kept in one database together with each customer's history, not spread across email, a spreadsheet and the payment dashboard.
How much fake orders cost
A fake caught before shipping costs staff time; a fraudulent order that ships and ends in a chargeback costs the goods, the shipping and the dispute fee. Hence the formula:
Illustrative example for the arithmetic; only the dispute fee is a real figure (Stripe's €20 fee in its Ireland price list, checked on October 31, 2026). A store gets 600 orders a month. A manager cancels 30 fakes, spending 6 minutes on each at €0.50 a minute (€30 an hour). Four fraudulent card orders pass the checks, ship, and come back as fraud disputes; each order had goods costing €60 and shipping of €8.
| Line | Count | Per item, € | Total, € |
|---|---|---|---|
| Checking and cancelling fakes | 30 | 3 | 90 |
| Goods lost on chargebacks | 4 | 60 | 240 |
| Shipping paid on chargebacks | 4 | 8 | 32 |
| Dispute fees | 4 | 20 | 80 |
| Total | 442 |
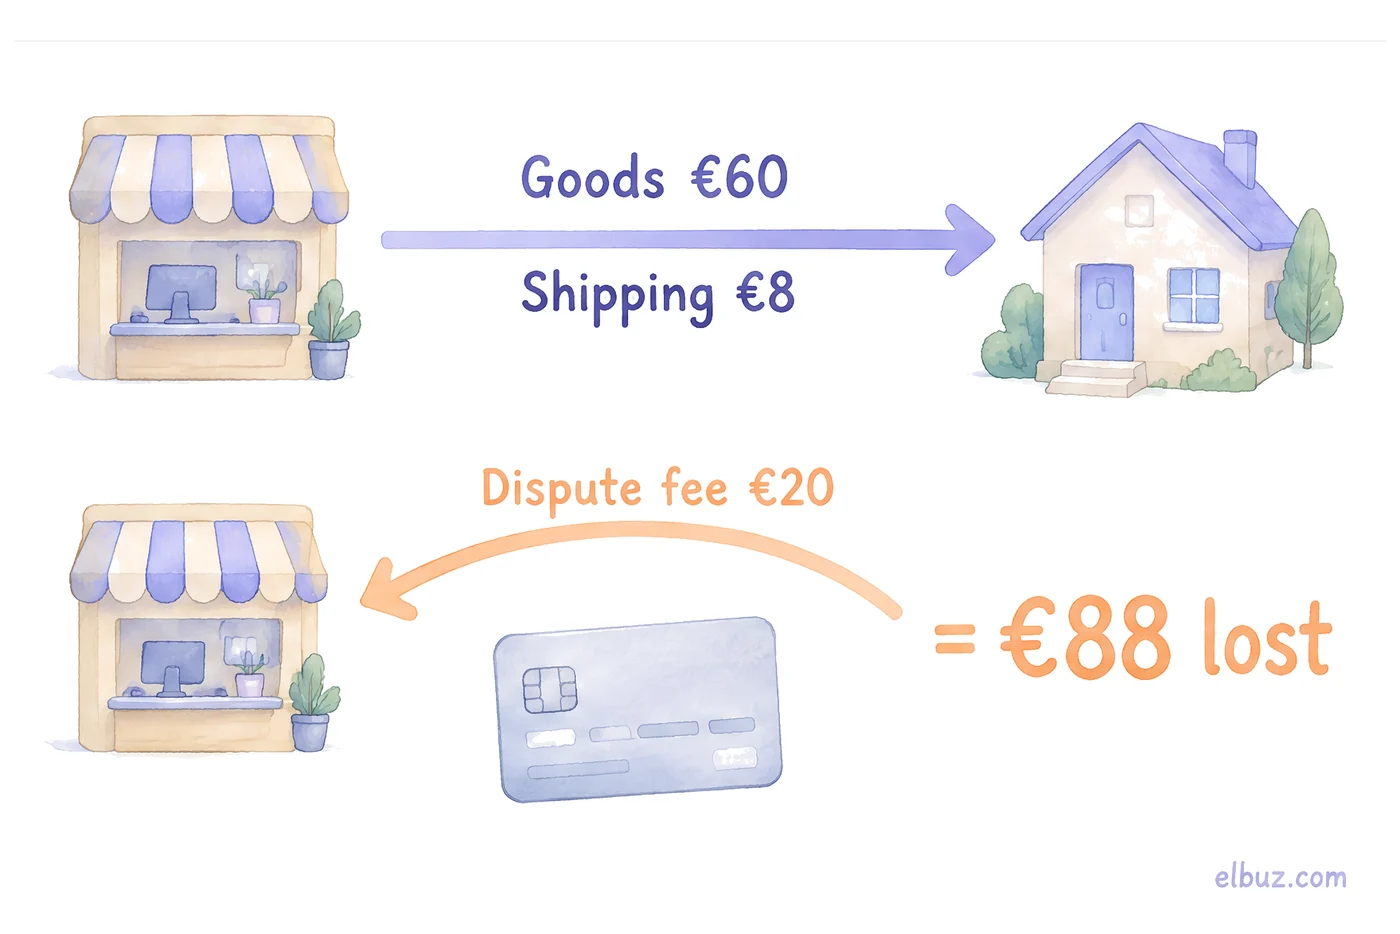
Chargebacks account for €352 of the €442, about 80%. If the store keeps €15 of profit per order, one chargeback at €88 wipes out the profit of almost six real orders, and the whole month of fakes about 30. That is why it matters more to stop risky orders before shipping than to catch every bot. If you also accept cash on delivery, refused parcels add a similar line; costs and the share of refusals are covered in the article on cash on delivery for ecommerce.
How to stop fake orders without scaring off real customers
Put the checks in layers so that each one stops its own kind of fake, and an honest buyer passes them without noticing. Use the strict checks only where the risk is higher.
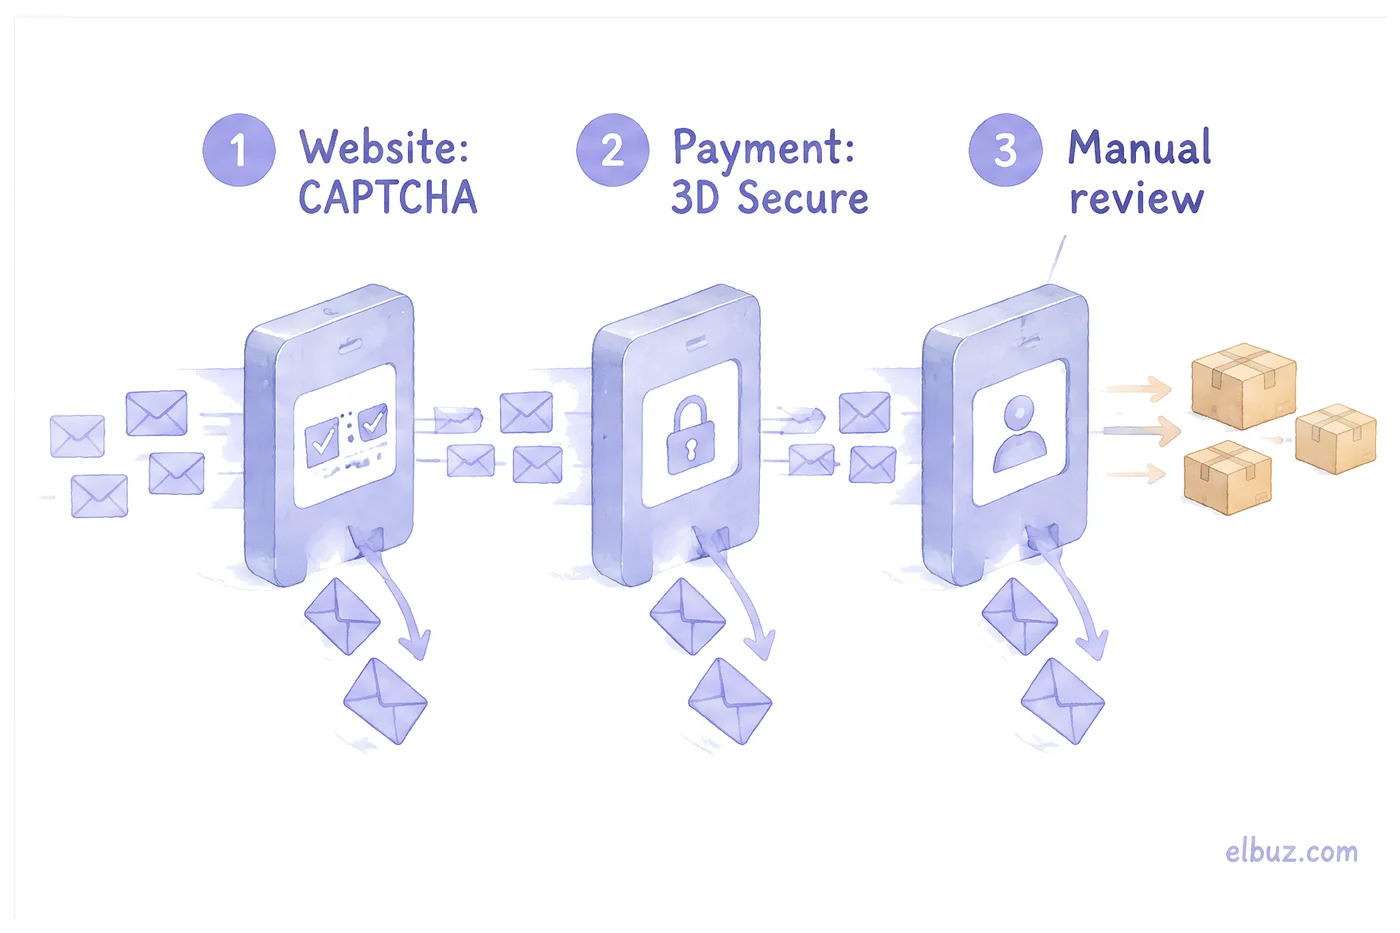
| Check | What it stops | Cost for an honest buyer |
|---|---|---|
| Invisible CAPTCHA (reCAPTCHA v3) | spam bots, card-testing scripts | none: it scores the request without a task for the person |
| Hidden form field | simple bots that fill in every field | none |
| Phone and address validation | impossible numbers, made-up addresses | none |
| Rate limits per IP, email and card | bursts of orders, card testing | rare: a wholesale buyer writes to you |
| 3D Secure for risky payments | payments with stolen cards | a confirmation in the banking app |
| Manual review before shipping | orders with two or three signs from the list | a delay of a few hours |
| Login required before payment | card testing through guest checkout | an extra step; use only during an attack |
Invisible CAPTCHA: reCAPTCHA v3 gives every request a score from 0.0 (very likely a bot) to 1.0 (very likely a good interaction), and Google suggests starting with a threshold of 0.5. You do not have to block low scores: you can send those orders to manual review.
3D Secure: when a fraudulent payment was successfully authenticated with 3D Secure and the cardholder disputes it as fraud, the liability typically shifts from you to the card issuer. Stripe stresses that this is not guaranteed for every payment. In the EU, Strong Customer Authentication already triggers 3D Secure for many card payments; you can also request it for orders that look risky. How card fees and acquiring work in general is covered in the article on merchant acquiring for online stores.
Fraud schemes by real customers
Unlike a bot, a fraudulent buyer places a normal order; the fraud shows up later, on payment, delivery or return. The most common schemes:
- Friendly fraud. The customer received the goods but disputes the card payment as unauthorised or "not received". Keep the tracking number and proof of delivery with the order: for disputes, payment providers ask what was ordered, how it was delivered and to whom.
- "The parcel never arrived." The same claim made to you instead of the bank. The answer is the carrier's delivery status; for valuable orders, ship with a signature.
- Swapped returns. The customer returns a cheaper copy or an item with a different serial number. Record serial numbers and photograph valuable goods before shipping.
- Return after use. An item worn once comes back as "did not fit". State return conditions on the website and check the item before refunding.
- Fake payment proof. For bank transfers: a screenshot of a "payment" that never arrives. Ship only after the money is on your account.
If the loss is large or the scheme repeats, report it: in the United States to the FBI's Internet Crime Complaint Center (IC3), in the EU to the cybercrime unit of your national police. Tell your payment provider as well.
When customer history should be in the order record
When there are dozens of orders a day, nobody remembers which customer already filed a chargeback or ordered the same thing twice yesterday. The most reliable sign from the list, the customer's history, works only if it is on the screen while the order is being checked.
In Elbuz each order is linked to the customer record, so the purchase history is one click away. The order form shows a "Possible duplicate" warning when the same customer already has a similar order within seven days, with the same amount or the same external order number. If you accept cash on delivery, the order also shows a "Non-redemption risk" warning with the share of COD parcels this customer has actually collected and a suggestion to ask for prepayment or confirm the order by phone.
The limits: Elbuz does not score card payments; that is the job of your payment provider's fraud tools and of 3D Secure. And a first order from a new contact has no history to compare with. How orders, customers and shipping come together in one database is shown on the ecommerce CRM page.
Orders and customer history in ElbuzDuplicates and risky customers are visible before you ship
Frequently asked questions
What are fake orders?
Orders in an online store that nobody intends to pay for honestly: from bots, card testers, pranksters, competitors or affiliates inflating their numbers. They take up staff time, and if they ship, they cost the goods, the shipping and the chargeback fees.
What is card testing?
Fraudsters use your checkout to find out which stolen card numbers still work, usually with small payments made by scripts. Typical signs are a spike in declined payments and small orders with nonsense names and emails.
How do I stop bots from placing orders?
Add an invisible CAPTCHA such as reCAPTCHA v3, a hidden field that only bots fill in, phone and address validation, and rate limits per IP address, email and card. Real customers do not notice these checks.
Should I cancel a suspicious order?
Not straight away. Hold it and check it: if two or three warning signs match and the customer does not confirm the order, cancel and refund it before shipping, which costs less than a chargeback later.
What is friendly fraud?
A customer who received the goods disputes the card payment as unauthorised or not delivered. Proof of delivery and a clear order history are your main evidence in the dispute.
How much does a chargeback cost a merchant?
The lost goods and shipping plus the provider's dispute fee; Stripe, for example, charges €20 per dispute in its Ireland price list. See the calculation for a full example.
Where do I report a fraudulent customer?
In the United States, to the FBI's Internet Crime Complaint Center (IC3); in the EU, to the cybercrime unit of your national police. Attach the order, the shipping details, your messages and the payment records, and inform your payment provider.
Sources
- Stripe — card testing: how it works, signs, prevention (CAPTCHA, rate limits, limiting access to the payment form) — docs.stripe.com/disputes/prevention/card-testing.
- Stripe — 3D Secure, Strong Customer Authentication and liability shift — docs.stripe.com/payments/3d-secure/authentication-flow.
- Stripe — pricing, Ireland: dispute fee €20.00 — stripe.com/en-ie/pricing.
- Google reCAPTCHA v3 — score from 0.0 to 1.0, threshold 0.5 — developers.google.com/recaptcha/docs/v3.
- FBI Internet Crime Complaint Center (IC3) — ic3.gov.
Checked on October 31, 2026. All other numbers in the article are illustrative examples for the arithmetic.


